 Vault
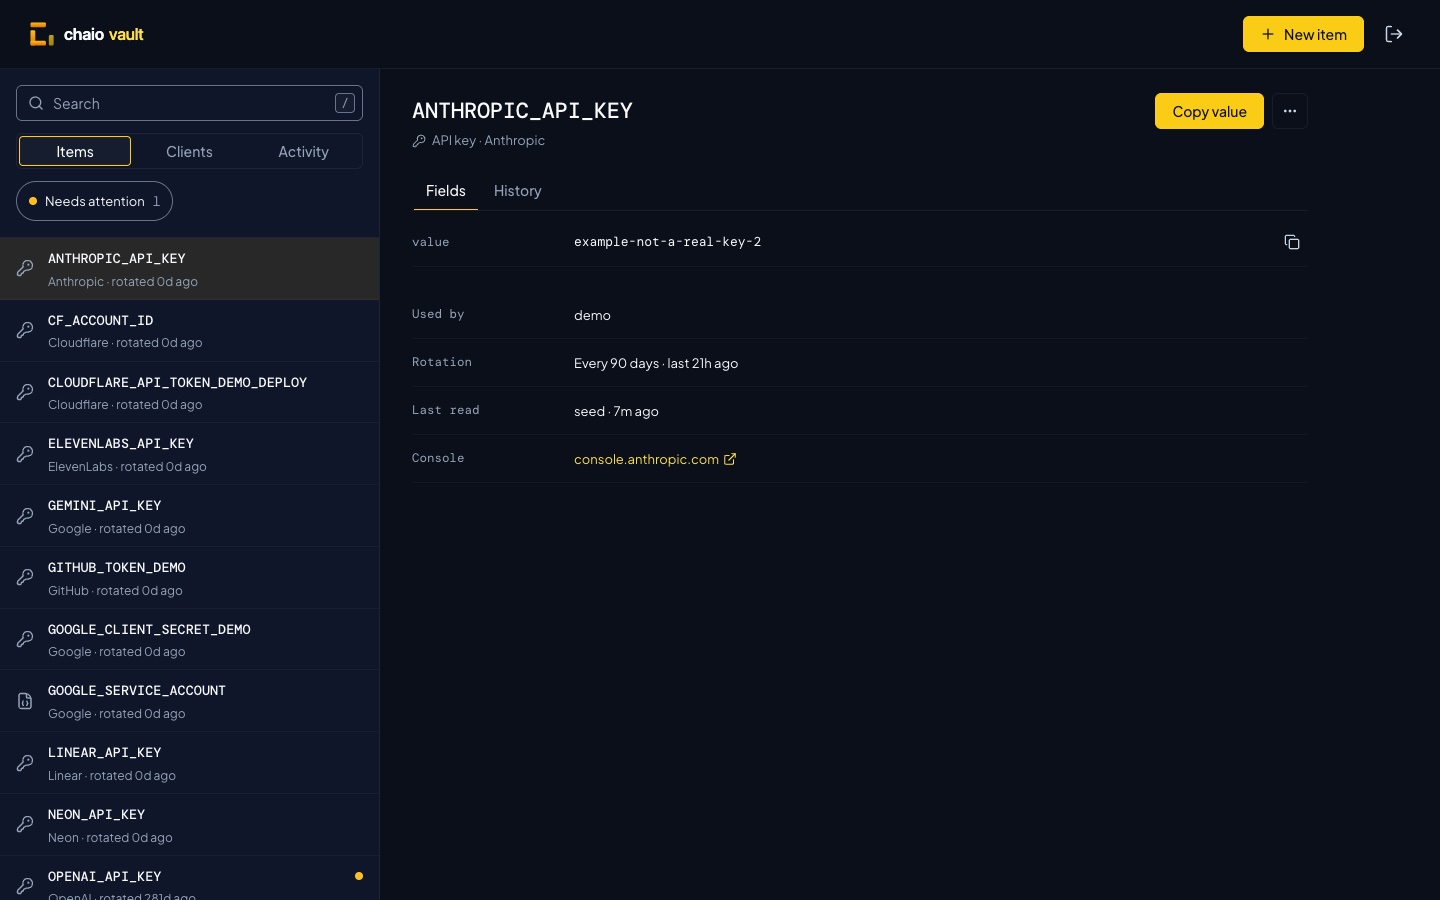
What if your secrets stayed out of your code and your chats?
Every key and password in one list, handed to your programs and agents when they run, with a record of who read what.
Rotate
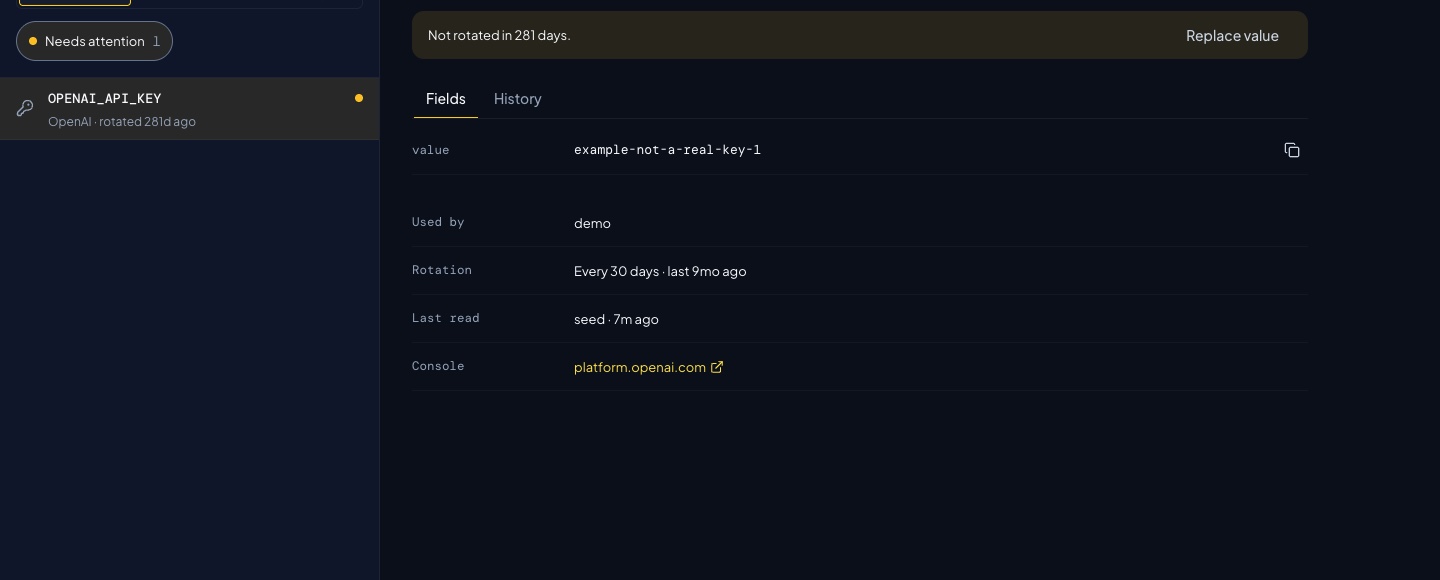
Know what's overdue before it bites.
Vault flags failed pushes, overdue rotations and anything you've stopped using. When it's time, it walks you through the change and pushes the new value out.
Control
Give every script its own key, and take it back.
Scripts and agents each get their own access. Revoke it at any time, and see exactly what it did.
And everything around it.
Your program gets the secret
Run a program through Vault and it receives what it needs, without the value landing in your terminal or your chat.
Everything has a place
API keys, credentials files, databases, SSH keys, logins, Wi-Fi, recovery codes and notes.
Keeps its history
See past versions of a secret and restore an older one.
A full record
See who did what to which secret, without the values.
Pushes to Cloudflare
Send a secret to a Cloudflare Worker when you save it, or on demand.
Bring what you have
Import your existing secrets, or move across from Doppler.
Straight answers.
Is it end-to-end encrypted?
No. It encrypts on the server, and the service decrypts a value when it's read. It's not end-to-end or zero-knowledge.
Can a program read my secret?
Yes. A program you give a secret to can read it, so give each one only what it needs.
Does it work through MCP?
No. Vault works from the command line and the web.
Can my team use it?
Not yet. It's for one person today, with no teams or sharing.
Does it rotate keys for me?
It guides you through it. Automatic rotation isn't built yet.
What if you never pasted a key into a chat again?
Vault is invite only for now. One Chaio account signs you in.